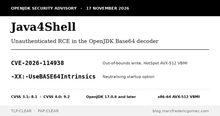
Java4Shell, CVE-2026-114938, enables unauthenticated RCE through the OpenJDK Base64 decoder on x86-64 servers that support AVX-512 VBMI.
Java4Shell, CVE-2026-114938, enables unauthenticated RCE through the OpenJDK Base64 decoder on x86-64 servers that support AVX-512 VBMI.
On 10 November 2026, the US agency CISA adds six exploited vulnerabilities to its catalogue, including two Barracuda Email Security Gateway vulnerabilities that, when chained, give root access without authentication and whose exploitation is confirmed by the vendor. The other four affect Chromium, Outlook, Cisco BroadWorks and Openwave Webtop; for BroadWorks, no public source yet…
On 10 November 2026, Microsoft fixes 1,093 vulnerabilities, its second-largest monthly release after October’s record, and only one of them is exploited: CVE-2026-124194, a spoofing flaw in Outlook that hands the user’s NTLMv2 hash to the attacker. The US agency CISA added it to its catalogue the same day, with a deadline of 24 November;…
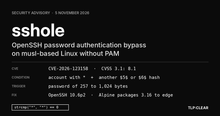
On 5 November 2026, OpenSSH issued emergency release 10.6p2 to block sshole, CVE-2026-123158: on a musl-based Linux system without PAM, Alpine Linux among them, an account with no password accepts any password between 257 and 1,024 bytes long. Previdian reports a first exploitation attempt less than nine hours after the CVE was published, and root…
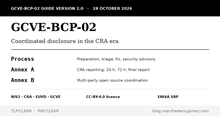
Published on 28 October 2026, version 2.0 of the GCVE-BCP-02 guide describes vulnerability handling and coordinated disclosure as a complete operational process, from preparation to lessons learned, and ties it to the reporting obligations of the European Cyber Resilience Act. It adds an annex on coordination between upstream projects, distributions, integrators and manufacturers in open source ecosystems.
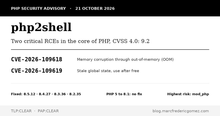
On 21 October 2026, the PHP project issued emergency fixes for php2shell, two critical vulnerabilities in the core of the engine, CVE-2026-109618 and CVE-2026-109619, which allow unauthenticated remote code execution across every web serving mode. The unsupported branches, from PHP 5 to PHP 8.1, are listed as affected by CERT-FR but absent from the CVE records, and receive no fixed release.
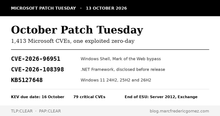
Microsoft publishes 1,413 CVEs on 13 October 2026, above September’s 973. Only one is exploited, a Mark of the Web bypass added the same day to CISA’s KEV catalogue, and this Patch Tuesday is the last one scheduled under the ESU programmes for Windows Server 2012, 2012 R2, Exchange Server 2016 and 2019. TLP:CLEAR …
Ten agencies from seven countries document how Integrity Technology Group, a Chinese company sanctioned by the US Treasury since January 2025, supplies automated scanners, botnets, hijacked VPNs and exfiltration scripts to actors linked to Flax Typhoon. Eight old vulnerabilities, five of them just added to CISA’s KEV catalogue, remain successfully exploited.
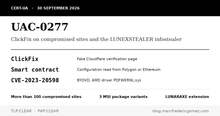
Ukraine’s government incident response team describes a ClickFix campaign served from more than a hundred compromised sites and steered through a smart contract. One of its three installation chains loads a vulnerable AMD driver whose sample does not appear in the April 2026 copy of the Microsoft blocklist examined here.
CVE-2026-19490 is a SAML authentication bypass on NetScaler, not the two RCE zero-days disclosed on 26 September. Here is how to tell them apart.
CISA officially migrated its Coordinated Vulnerability Disclosure (CVD) platform on September 17. Behind the acronym VINCE-NT (Vulnerability Information and Coordination Environment – New Technology), which replaces the venerable VINCE operated since 2020 by the CERT/CC, lies much more than a mere interface facelift or a welcome alignment with CSAF status frameworks. This is an act…
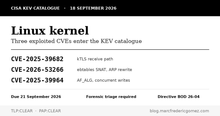
Three Linux kernel CVEs enter CISA’s KEV catalogue with a three-day deadline and mandatory forensic triage. Fixes, scope and how to read the scores.
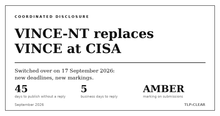
CISA switched its coordinated disclosure platform on 17 September. TLP marking, a 45-day clock, sanctions screening: the rules are written.