Tag: ENISA

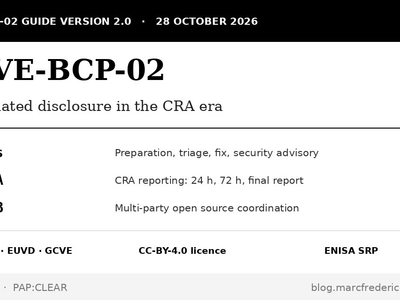
GCVE-BCP-02: coordinated disclosure in the CRA era

Published on 28 October 2026, version 2.0 of the GCVE-BCP-02 guide describes vulnerability handling and coordinated disclosure as a complete operational process, from preparation to lessons learned, and ties it to the reporting obligations of the European Cyber Resilience Act. It adds an annex on coordination between upstream projects, distributions, integrators and manufacturers in open source ecosystems.
Comparative review of cybersecurity taxonomies used by CSIRTs, CERTs, and SOCs

Executive summary CSIRTs, CERTs, and SOCs rely on incident and threat taxonomies to classify, analyze, and share cybersecurity information consistently. This article compares the principal taxonomies in use—eCSIRT.net, ENISA’s Reference Incident Classification Taxonomy and Threat Taxonomy, FIRST’s CSIRT case classification guidance, MISP taxonomies, VERIS, and MITRE ATT&CK—covering their origins, structure, operational uses, strengths, limitations, and…