Tag: KEV

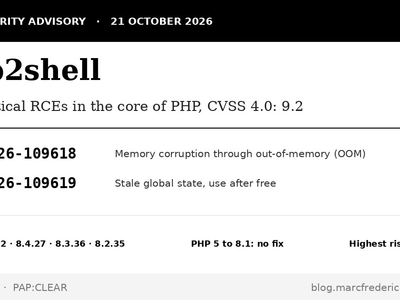
php2shell: two critical RCEs in the core of PHP

On 21 October 2026, the PHP project issued emergency fixes for php2shell, two critical vulnerabilities in the core of the engine, CVE-2026-109618 and CVE-2026-109619, which allow unauthenticated remote code execution across every web serving mode. The unsupported branches, from PHP 5 to PHP 8.1, are listed as affected by CERT-FR but absent from the CVE records, and receive no fixed release.
VINCE-NT and the Nationalization of the Bug: When CISA Cuts the Academic Cord

CISA officially migrated its Coordinated Vulnerability Disclosure (CVD) platform on September 17. Behind the acronym VINCE-NT (Vulnerability Information and Coordination Environment – New Technology), which replaces the venerable VINCE operated since 2020 by the CERT/CC, lies much more than a mere interface facelift or a welcome alignment with CSAF status frameworks. This is an act…