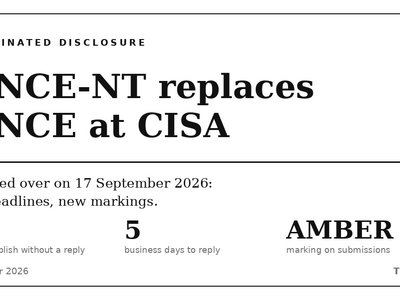
CISA officially migrated its Coordinated Vulnerability Disclosure (CVD) platform on September 17. Behind the acronym VINCE-NT (Vulnerability Information and Coordination Environment – New Technology), which replaces the venerable VINCE operated since 2020 by the CERT/CC, lies much more than a mere interface facelift or a welcome alignment with CSAF status frameworks.
This is an act of sovereignty. The U.S. government is reclaiming total control over the global vulnerability management infrastructure. This shift speaks volumes about the growing militarization and bureaucratization of our ecosystem.
The End of the Academic Trusted Third Party
To fully grasp the magnitude of this migration, we must remember where we came from. VINCE was historically operated by the CERT/CC. The CERT/CC (the Software Engineering Institute at Carnegie Mellon University) is the historic cradle of incident response, born in 1988 following the Morris worm crisis. For over three decades, it embodied a neutral, academic, almost university-like trusted third party. It was a unique space where researchers, vendors, and government agencies interacted as peers under the banner of science and technical collaboration.
With VINCE-NT, CISA now hosts and administers the tool entirely on its own. The cord has been cut. The management of the tech industry’s most critical secrets—non-public vulnerabilities—now falls under the exclusive and direct control of the U.S. Department of Homeland Security (DHS). Cyber defense is definitively leaving its collaborative adolescence behind to enter the era of state-managed control.
The Sovereignty Funnel: An Inevitable Parallel
This internalisation movement is by no means an isolated incident. It perfectly fits into a broader, heavy trend of states regulating and reclaiming control over the threat landscape.
It is impossible not to draw a parallel with China. In 2021, Beijing implemented strict regulations forcing local security researchers to report any discovered vulnerability to the MIIT (Ministry of Industry and Information Technology) before any international publication, effectively banning direct disclosure to Western vendors.
CISA’s approach with VINCE-NT is admittedly more transparent, codified, and aligned with market standards (CSAF, CVE). However, the end goal remains identical: creating a state-run funnel. The U.S. administration is centralizing the pipeline to feed its own prioritization engines, starting with its KEV (Known Exploited Vulnerabilities) catalog and its emergency directives.
The TLP:AMBER+STRICT Trap
This structural takeover comes with a significant tightening of confidentiality rules. Accessing VINCE-NT now requires vetting participants and strictly tagging data. While an initial submission by a reporter remains TLP:AMBER, all subsequent exchanges, coordination discussions, and the internal lifecycle of the flaw are placed under the hammer of TLP:AMBER+STRICT.
For CERTs and Cyber Threat Intelligence (CTI) teams, the impact is immediate. This airtight compartmentalization strictly forbids any external dissemination or sharing. CISA is bunkerizing the data. The community’s spontaneous, informal mutual aid is fading away, replaced by a state administrative procedure where the regulator becomes the sole legitimate filter of what gets out, and when.
What This Changes for Us (We don’t overthink. We adapt the pipelines.)
On a purely operational level, this shift is a necessary step toward industrialization. The native adoption of CSAF terminology (where Vendor becomes Supplier, and Product becomes Component) will finally clean up data streams. For a CERT, this ensures the ingestion of security advisories that are directly machine-readable, making internal scoring easier and accelerating remediation.
But on a strategic posture level, it forces two realities upon us:
- The clock is ticking: VINCE-NT introduces a strict five-business-day response SLA for participants. If a component in your infrastructure is affected and you are looped into the case, your teams will no longer have time to procrastinate.
- Technological dependency: By centralizing global CVD, CISA is positioning itself as the ultimate single window for vulnerability management. In the long run, this raises serious questions about the room left for European initiatives (ENISA, national CERTs) to govern these critical data flows.
The cyber Wild West is officially dead. Welcome to the era of state-run vulnerability bureaus.